Aviation cybersecurity is the protection of aviation systems, operational data, passenger information, aircraft-adjacent technology, airport infrastructure, supplier integrations, and software workflows from cyber threats. The real issue is not just data loss. It is safety, operational continuity, passenger trust, regulatory exposure, and the ability to keep flights, facilities, and support teams moving when digital systems are under pressure.
Aviation cybersecurity at a glance
Aviation cybersecurity is the discipline of protecting aviation systems, data, networks, and operational workflows from digital threats that can disrupt safety, scheduling, compliance, or customer trust. Treat it as an operational risk program, not a narrow IT task. The table below connects common exposure areas with practical control priorities.
| Risk area | Affected systems | Likely impact | Control priority |
|---|---|---|---|
| Airline operations | Crew systems, scheduling, dispatch, flight operations tools | Delays, manual workarounds, disrupted decision-making | Identity controls, monitoring, recovery plans, access reviews |
| Airport systems | Baggage, gates, kiosks, facility systems, operational networks | Passenger disruption, throughput loss, service outages | Network segmentation, vendor access control, asset inventory |
| Passenger data | Booking, loyalty, check-in, mobile apps, payment flows | Privacy exposure, fraud, trust loss | Encryption, least privilege, secure APIs, audit trails |
| Connected aircraft and ground systems | Maintenance links, ground-support tools, data transfer workflows | Safety-adjacent risk, operational delay, integrity concerns | Segmentation, controlled interfaces, integrity checks |
| MRO and engineering | Maintenance records, manuals, parts data, inspection workflows | Compliance gaps, inaccurate records, downtime | Access governance, change control, offline access, evidence capture |
| Cloud and data platforms | Data lakes, analytics, integrations, AI models, reporting | Data leakage, misconfiguration, poor visibility | Secure cloud architecture, logging, secrets management |
| Supplier ecosystem | APIs, managed services, vendors, partners, contractors | Lateral movement, weak controls outside direct ownership | Supplier risk reviews, contractual controls, continuous monitoring |
The main lesson is simple: aviation cybersecurity cannot be scoped only around firewalls or endpoint tools. It must cover the workflows that keep aircraft, airports, crews, passengers, and compliance teams connected. A single weak integration, unmanaged identity, or untested recovery process can create pressure far beyond IT.
Where aviation cybersecurity risk actually shows up
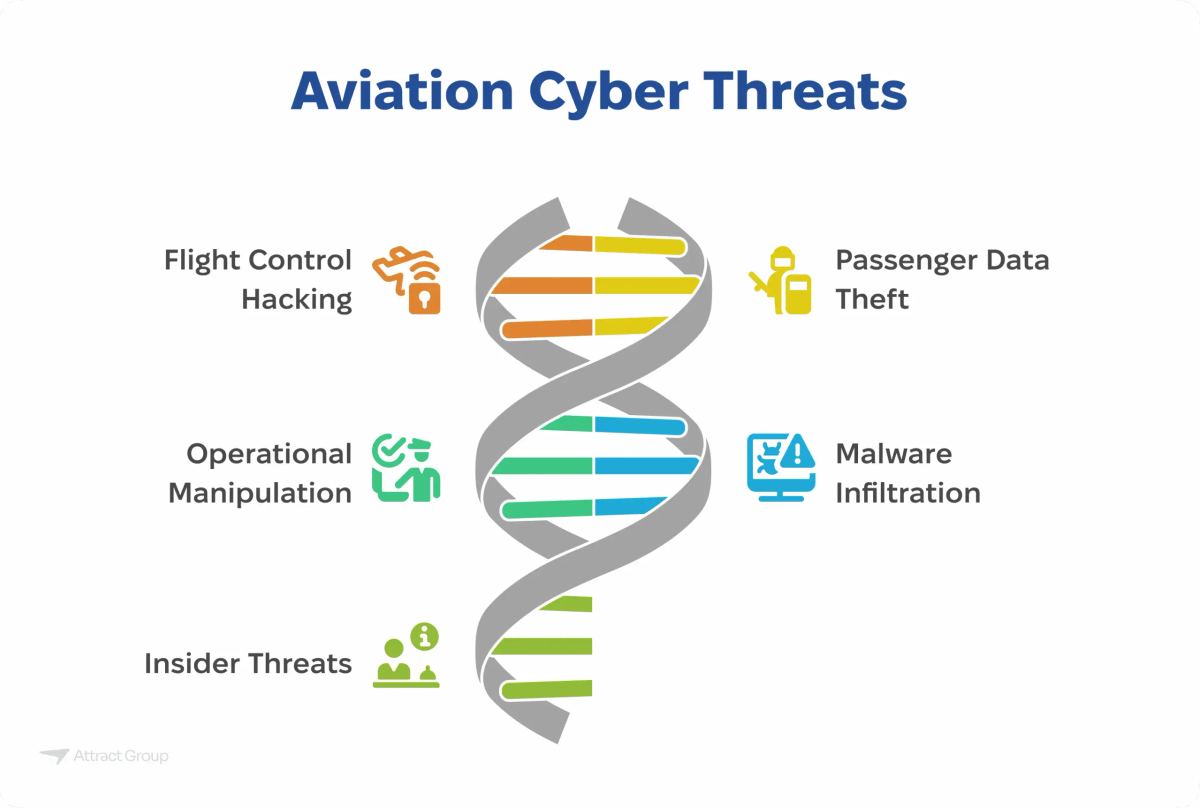
Most aviation cyber security risks appear where operational systems, passenger-facing services, vendors, and data platforms meet. A modern airline or airport rarely has one isolated attack surface. Risk moves through identity, APIs, mobile apps, ground equipment, cloud environments, partner connections, and staff workflows.
Airline operations
Airline cybersecurity starts with systems that support daily operations: crew scheduling, dispatch coordination, load planning, maintenance planning, customer notifications, loyalty accounts, mobile check-in, and internal communications. Attackers do not need to reach avionics to cause damage. Disrupting scheduling, identity, operational dashboards, or passenger self-service tools can create delays and manual overload. Airlines should treat operational applications as business-critical systems with defined owners, tested recovery steps, and documented data flows. Controls should include multi-factor authentication, role-based access, privileged access management, secure APIs, strong logging, and tested fallback procedures.
Airport systems
Airport cybersecurity covers a broad mix of systems: passenger processing, baggage handling, gates, kiosks, parking, access control, building systems, operational screens, Wi-Fi, and vendor-managed platforms. Many airports work with airlines, government agencies, retailers, ground handlers, and facility contractors, which makes supplier access a major concern. The risk is not only data theft. Airport disruption can quickly affect passenger flow, airline schedules, and public confidence. Segmentation, asset inventory, vendor access review, network monitoring, and recovery procedures should be treated as operating requirements, not optional IT tasks.
Passenger data and digital trust
Passenger data flows through booking engines, travel management platforms, airline apps, loyalty programs, payment systems, call centers, and airport services. Names, travel patterns, identity documents, payment references, accessibility needs, and loyalty profiles can all become sensitive when combined. Encryption is necessary, but it is not enough on its own. Teams need clear data classification, minimal data retention, access controls, secure API design, tokenization where suitable, audit logs, and tested breach response playbooks. Passenger trust depends on both prevention and transparent response.
Connected aircraft, ground systems, and data transfer
Aviation technology increasingly depends on connected workflows between aircraft, ground operations, maintenance teams, and analytics platforms. That does not mean every connected system has the same risk, but it does mean every interface needs clear boundaries. Teams should document which systems exchange data, who can access them, how integrity is checked, how updates are controlled, and what happens during degraded connectivity. Secure design should reduce the chance that an issue in one system can move into another.
MRO, manuals, and engineering workflows
Maintenance, repair, and overhaul teams rely on accurate records, manuals, inspections, approvals, and parts information. Cyber risk in this area often shows up as data integrity risk: the wrong record, missing evidence, unauthorized change, or inaccessible workflow during time-sensitive work. Secure MRO workflows need role-based permissions, version control, audit trails, offline capability where field conditions require it, and clear approval paths. These controls support compliance and reduce rework when records must be reviewed later.
Vendor integrations and cloud data platforms
Aviation software often depends on vendors for booking, payments, operational data, analytics, communications, and infrastructure. Each integration should be reviewed for authentication, authorization, logging, data minimization, rate limits, and ownership of incident response duties. Cloud platforms can improve resilience when designed well, but they can also create risk through misconfigured storage, weak identity policies, exposed APIs, and poor separation between environments. Secure cloud architecture, automated configuration checks, monitored pipelines, and regular access reviews are baseline requirements. AI and machine learning can support anomaly detection, predictive maintenance, fraud review, and operational analysis. They should not be treated as replacements for control design. Teams need governed data access, model monitoring, explainable workflows for sensitive decisions, and human review where operational impact is high.
Regulatory and compliance drivers aviation teams cannot ignore
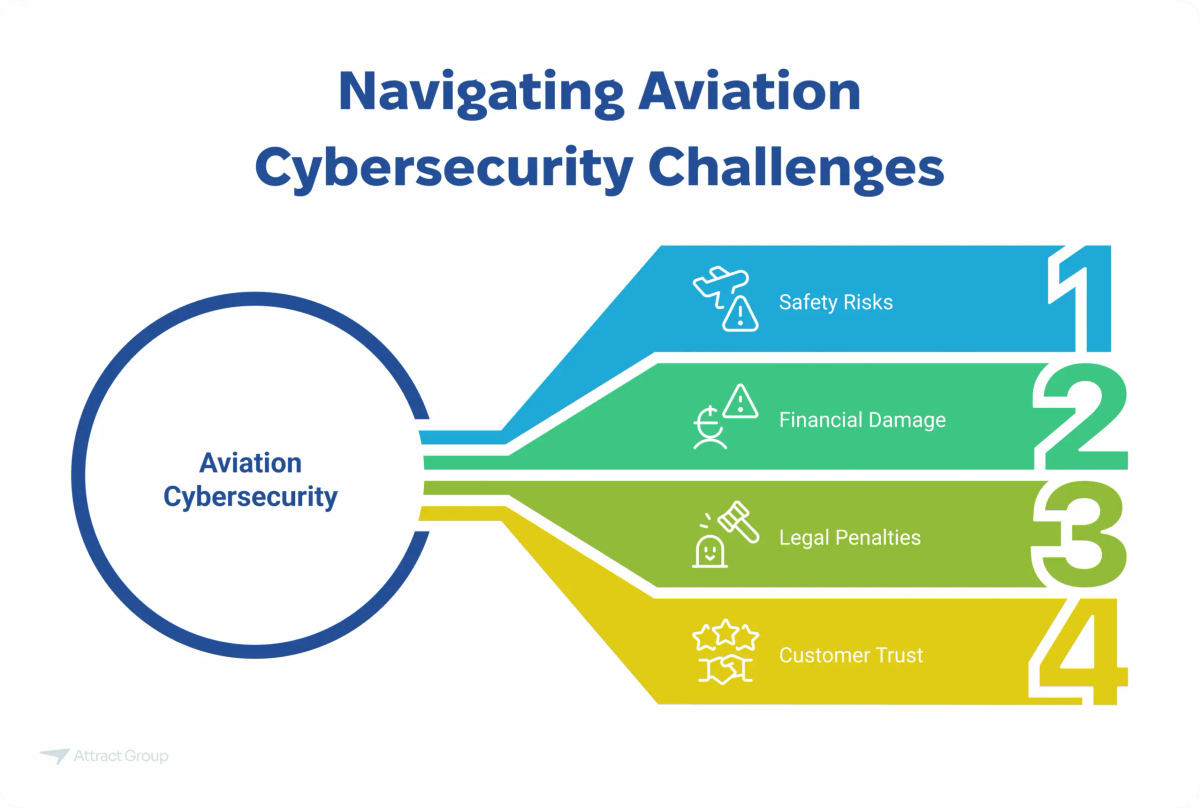
Compliance does not replace security, but it gives aviation teams a structure for accountability. Aviation cybersecurity compliance now reaches beyond privacy and payment controls into safety-impacting information security risk management. Operators, airports, software vendors, and suppliers should map obligations early, then keep evidence ready for audits and oversight. The ICAO aviation cybersecurity work includes Annex 17 cybersecurity SARPs, guidance, capacity support, and the 2025 Assembly Resolution A42-19. ICAO's Aviation Cybersecurity Strategy is organized around seven pillars: international cooperation, governance, effective legislation and regulations, policy, information sharing, incident management and emergency planning, and capacity building and culture. For organizations within EASA scope, the EASA Easy Access Rules for Information Security cover Regulation (EU) 2022/1645 and Regulation (EU) 2023/203. These rules address information-security risks with potential impact on aviation safety and require an information security management system for covered organizations. U.S. aviation teams should account for TSA, CISA, and relevant federal guidance where applicable. The practical approach is to map each obligation to systems, owners, controls, evidence, and review cycles. Avoid treating compliance as a document exercise. The control either exists in operations, or it does not. A useful example is the Nimbl / AviationManuals platform, which turns compliance-heavy work into controlled web and mobile workflows. The platform supports manuals, risk assessments, LOA workflows, SMS tools, and mobile access. The portfolio notes a partnership since 2021, 55,000+ flights reviewed per year, 4,700+ operators, 6,000+ manuals and documents per year, and 30+ years of compliance experience. Do not infer cyber outcomes from those figures. The relevant lesson is workflow control: aviation compliance becomes more manageable when records, approvals, access, and evidence live in structured systems.
Controls that matter in aviation software and operations
Controls matter when they lower real operational risk, reduce blast radius, and give teams evidence they can act on. In aviation, that means protecting identity, data flows, safety-adjacent systems, mobile tools, APIs, and suppliers while keeping operations running during outages, degraded connectivity, or an active incident. Start with identity and access. Require multi-factor authentication for administrative and remote access. Use least privilege, strong joiner-mover-leaver processes, privileged access management, and regular access reviews. Service accounts should be owned, monitored, and rotated. Dormant accounts should be removed quickly. Segment networks and environments. Airport operational systems, corporate IT, development environments, cloud workloads, and vendor access should not sit in one flat network. Segmentation reduces blast radius and gives responders more options during an incident. Build secure software from the start. Aviation product owners should require secure SDLC practices: threat modeling, code review, dependency scanning, secure secrets handling, environment separation, vulnerability management, and release gates. Teams building or modernizing aviation products can use Custom Software Development support to embed these practices into product delivery rather than add them late. Encrypt sensitive data in transit and at rest. Encryption should cover passenger information, operational records, documents, and sensitive integrations. It should be paired with sound access control and monitored data movement, because encryption alone does not stop misuse by an over-permissioned account. Monitor what matters. Central logging, anomaly detection, SIEM integration, endpoint telemetry, cloud audit logs, and API monitoring help teams detect suspicious behavior. Machine learning can support detection patterns, but it needs clean data and human response procedures. For model-driven workflows, AI Integration Services should include data governance and review paths. Plan incident response around operations. Aviation incident response cannot stop at technical containment. Playbooks should cover flight operations, passenger communications, airport partners, regulators, suppliers, legal teams, and executive decision-makers. Tabletop exercises should test both cyber steps and operational continuity steps. Manage supplier risk. Require security questionnaires, access limits, audit rights where suitable, incident notification terms, data handling terms, and periodic reviews. Supplier accounts should be monitored like internal accounts. Third-party APIs should have clear ownership and response paths. Design for offline resilience. Some aviation work must continue when connectivity is limited. The Vestergaard project is a practical example from de-icing operations: an offline-capable tablet app supports guided workflows, unit data, temperature and zone handling, job history, event logging, and traceable records. The cyber lesson is broader than de-icing. Offline capability, audit trails, and controlled sync can support operational continuity and evidence quality. Test recovery, not just backup. Backups are only useful when restoration works within acceptable timeframes. Teams should define recovery time objectives, recovery point objectives, clean restore procedures, manual fallback steps, and decision rights during a degraded state. DevOps & Cloud support can help structure infrastructure, monitoring, and recovery practices. Penetration Testing can test exposed systems, APIs, and application paths before attackers do.
How to scope an aviation cybersecurity roadmap
A roadmap should turn broad cyber concern into sequenced work that owners can fund, test, and repeat. Start with the systems that affect safety, airport throughput, airline operations, passenger trust, and regulatory evidence. Then phase controls so the organization can improve without stalling delivery.
| Phase | Main question | Output |
|---|---|---|
| Asset and risk inventory | What systems, data, integrations, and vendors support aviation operations? | System inventory, data map, owner list, risk register |
| Threat modeling | How could misuse, outage, or compromise affect operations? | Attack paths, misuse cases, risk ranking |
| Control baseline | Which controls must exist across identity, data, cloud, software, and vendors? | Baseline policy, control owners, implementation backlog |
| Compliance mapping | Which ICAO, EASA, U.S., privacy, and contract requirements apply? | Obligation-to-control matrix, evidence plan |
| Incident playbooks | Who acts when systems fail or compromise is suspected? | Playbooks, contact lists, escalation rules |
| Testing and recovery | Can the team detect, contain, restore, and operate in degraded mode? | Test reports, lessons learned, recovery improvements |
| Monitoring and governance | How will controls stay current as systems change? | Metrics, review cadence, supplier reviews, audit evidence |
A good roadmap has business owners, not just IT owners. Airline operations, airport operations, engineering, compliance, product, cloud, legal, procurement, and customer support all have a role. The best first step is often not a new tool. It is a clean inventory of systems, owners, integrations, and recovery expectations. The second step is threat modeling. Pick realistic scenarios: compromised vendor credentials, exposed passenger API, cloud storage misconfiguration, ransomware against corporate systems, unavailable MRO platform, tampered operational record, or loss of connectivity during field work. Rate each scenario by operational impact and recovery difficulty. The third step is control selection. Avoid a long checklist that no one owns. Select controls that can be implemented, tested, and evidenced. Each control should have an owner, scope, proof method, and review frequency. The fourth step is testing. Run tabletop exercises for operational incidents, not only IT incidents. Test data restoration. Test communications. Test manual workarounds. Test supplier notification paths. A plan that has never been exercised is only a document.
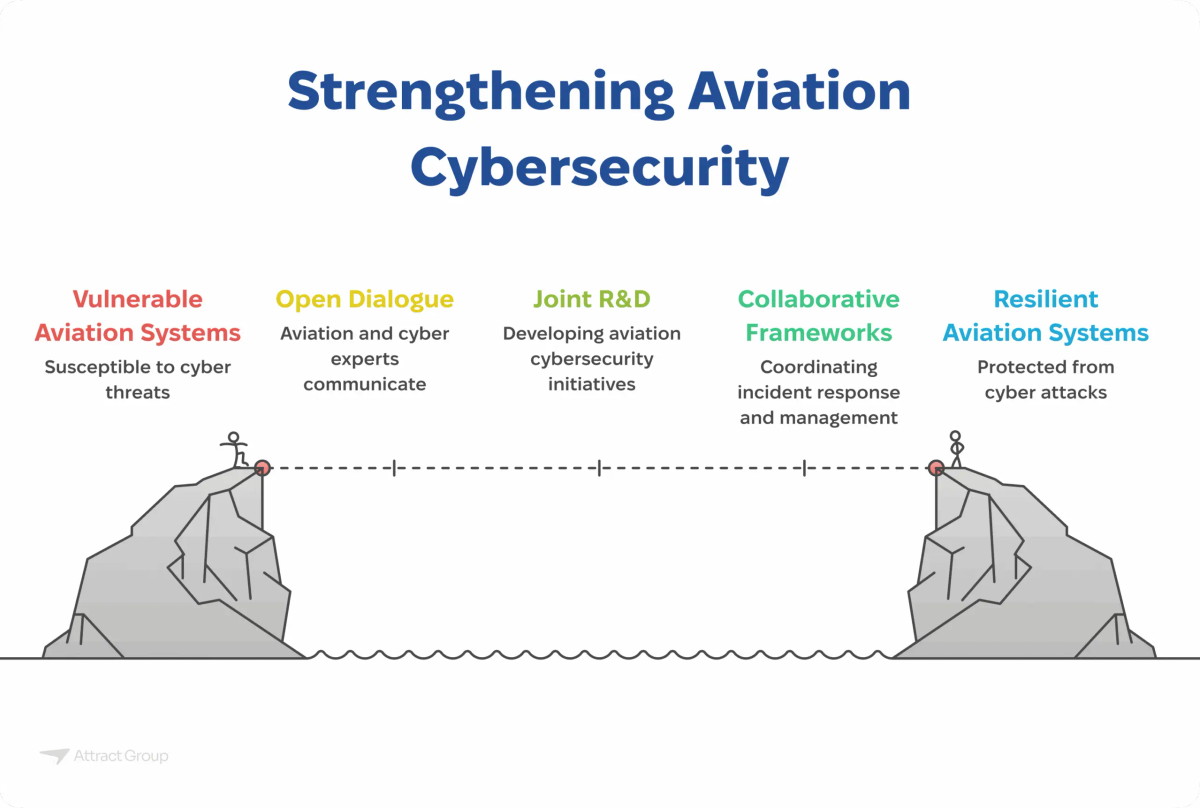
When to build custom aviation security tooling
Custom tooling makes sense when packaged products cannot reflect aviation workflows, offline field work, evidence needs, or complex integrations. Build only where it reduces manual control gaps or gives teams better operational visibility. For standard functions such as endpoint protection or SIEM, configure proven platforms first. Build custom software when teams need aviation-specific dashboards that combine operational status, cyber signals, supplier health, and compliance evidence. This can help leaders see which systems matter most, which controls are missing, and which incidents require cross-functional response. Custom compliance workflows can also be worth building when manual evidence collection slows audits or creates inconsistent records. Aviation teams often need controlled approvals, document versioning, risk assessments, mobile access, and traceable records. A well-designed workflow can reduce spreadsheet drift and give compliance managers a clearer evidence trail. Mobile and offline tools are another strong fit. Ground operations, inspections, de-icing, maintenance, and field support may not always have stable connectivity. Secure offline apps should support local data protection, user authorization, controlled sync, event logging, and conflict handling. Integrations are often the reason to build rather than buy. Airlines, airports, MRO providers, and aviation software vendors may need to connect legacy systems, cloud platforms, partner APIs, identity providers, and reporting tools. Custom integration work should include secure API design, logging, error handling, and supplier access controls.
The decision should be practical: buy commodity security capabilities, configure them well, and build only where aviation workflow, data, compliance, or resilience requirements demand a custom system.
FAQ
These questions come up when aviation teams move from concern to scope. Use them to separate risk ownership, compliance scope, and software decisions. The answers are concise by design, because the right next step usually depends on your systems, routes, suppliers, and operating model.
What is aviation cybersecurity?
Aviation cybersecurity protects aviation-related systems, data, networks, applications, operational workflows, and connected services from digital threats. It covers airlines, airports, MRO teams, ground-support operations, passenger systems, suppliers, cloud platforms, and aviation software products.
Why does aviation cybersecurity matter beyond IT?
Cyber incidents can affect scheduling, passenger processing, maintenance records, supplier access, airport throughput, regulatory evidence, and operational continuity. Even when safety-critical systems are isolated, disruption to surrounding systems can create material operational pressure.
What are common aviation cyber security risks?
Common risks include stolen credentials, ransomware, exposed APIs, cloud misconfiguration, weak supplier access, passenger data exposure, unpatched systems, poor logging, insecure mobile apps, and lack of tested recovery procedures.
How should aviation teams approach compliance?
Map applicable ICAO, EASA, U.S., privacy, contract, and internal requirements to specific systems, controls, owners, and evidence. Compliance should produce operating discipline, not just documents.
When should an aviation team consider custom security software?
Consider custom software when aviation-specific workflows, offline operations, compliance evidence, supplier integrations, or operational dashboards cannot be handled well by standard platforms. Build around clear control gaps and measurable operational needs.